Why Europe’s supermarket fridges were easy targets
 0
 0

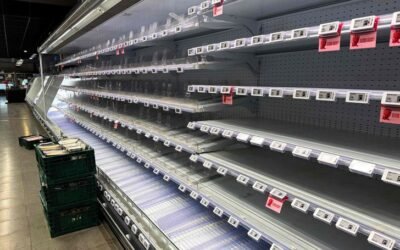
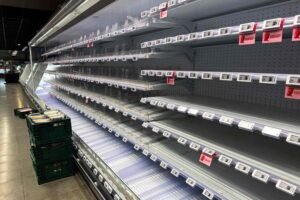
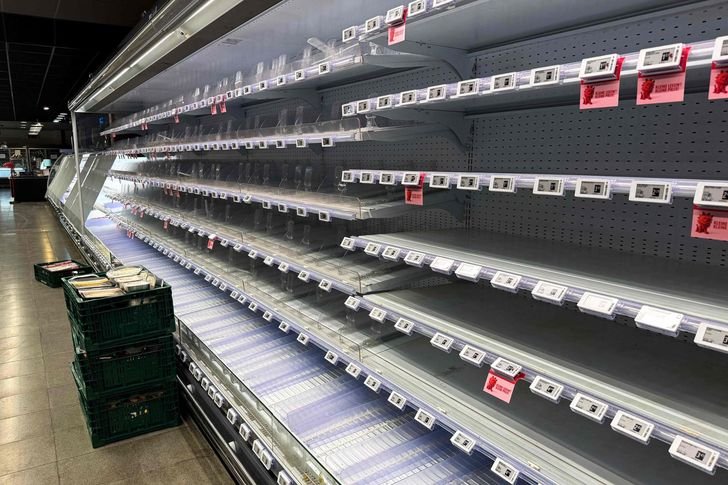
This photograph shows empty refrigerators in a Delhaize supermarket in Boortmeerbeek some 30 km from Brussels, Monday, following an IT incident. AFP-Yonhap
BRUGES, Belgium — Hackers who cranked up fridge temperatures at supermarkets across Europe may have gained access through public internet-connected systems protected by default passwords or outdated software, a cybersecurity expert said.
The second cyberattack in three weeks hit fridge systems at supermarket chains including Carrefour and Delhaize in Belgium, and ICA and Coop in Sweden, forcing retailers to discard spoiled food and raising concerns about food security. Three blood banks in France were also hit.
Authorities have not publicly disclosed how the attackers gained access, and no perpetrator has been identified.
Laurens Singier, an ethical hacker and researcher at Cyber 3 Lab, part of Howest University of Applied Sciences in Bruges, Belgium, said internet-connected systems which can be accessible remotely often have weak protections.
“In this case, the weak point was mainly putting those devices on the public internet. They shouldn’t even be there,” he said, speaking from a lab full of servers and systems similar to those that could control supermarket store fridges.
A common problem with such systems is that operators fail to change default passwords set by the manufacturer, while others run older software with known vulnerabilities, he said.
AI was now making it easier for amateurs to pull off hacks, Singier added.
Supermarkets on Tuesday said they had taken hacked fridges offline, in line with guidance from refrigeration monitoring software provider Danfoss, whose systems were again among those targeted. Danfoss has said it is working with clients on fixes.
Singier said that retailers should check they understand how they connect to the store interface, strengthen passwords, and consider switching from internet-based systems to more secure systems using SIM cards, like those used by solar panels and car chargers.
“After this attack, we’ve seen a lot less of these devices publicly on the internet,” he said. “But if you look at the numbers, there’s still a lot of industrial devices which are open to the public, and in a lot of cases you yourself as the butcher or the chocolatier don’t even know about it.”